OIM 11gR2 PS2 provides a convenient way of implementing this use-case and it is the subject of this post.
Showing posts with label OIM 11g. Show all posts
Showing posts with label OIM 11g. Show all posts
Wednesday, November 5, 2014
Implementing a Custom Landing Page in OIM
OIM 11gR2 PS2 provides a convenient way of implementing this use-case and it is the subject of this post.


Wednesday, June 25, 2014
Monitoring OIM R2 PS2 Orchestration
The OIM R2 PS2 (11.1.2.2.0) release provides a great new feature: monitoring of OIM orchestration processes through Enterprise Manager console.
Such feature provides the capability of querying orchestration data to check orchestration processes details. For example, you can check what happened during a user modification operation, or you can get details of failed orchestration processes, such details can help you to fix issues in your environment. It is also possible to check configuration information, like which event handlers are defined for a specific orchestration process.
Such feature provides the capability of querying orchestration data to check orchestration processes details. For example, you can check what happened during a user modification operation, or you can get details of failed orchestration processes, such details can help you to fix issues in your environment. It is also possible to check configuration information, like which event handlers are defined for a specific orchestration process.
Monday, January 27, 2014
OIM monitoring check-list
Systematic monitoring of OIM deployments helps to reduce risk of both technical and security related issues. It also can help to avoid performance degradation that can happen because of data growth over time.
This post presents a set of topics about OIM and WebLogic monitoring, and it presents tools that can be used for both monitoring and diagnostic.This list is not intended to replace any official product documentation, instead, it should be used in conjunction with it.
This is another post in the OIM academy series. You can check the complete series here.
This is another post in the OIM academy series. You can check the complete series here.
Tuesday, July 2, 2013
A checklist for OIM go-live
This post presents a list of configuration points in OIM that must be taken into account whenever a customer is planning an OIM go-live. This list is not intended to replace the OIM documentation, instead, the idea is to complement it. It provides tips on a few topics that are not part of the documentation.
Let's go for them:
Let's go for them:
Monday, June 17, 2013
Loading unique passwords with OIM bulk load
Using Oracle Identity Manager's bulk load tool is a great way to load large numbers of user records into OIM in an efficient and performant way. The standard and documented usage of the tool does not make provision for the loading of unique user passwords, though. This article describes an approach that can be used to achieve that requirement. This post is also part of the OIM 11g Academy Series.
Monday, January 28, 2013
Populating request attributes in OIM 11g R2 Part II - UI Customization
The approach describe in this post is more sophisticated when compared to the pre-populate plug-in described in the previous post. The emphasis here is UI interaction. It is also important to mention that this approach does not work for requests created through the APIs, it works only for UI based requests. Another difference is that while the pre-populated plug-ins are specific to request attributes, this approach is application instance specific. In other words, each different application instance request form will require a different customization.
Wednesday, January 23, 2013
Populating request attributes in OIM 11g R2 Part I - Prepopulate Plug-in
This is the first of a two posts series about pre-populating requests in OIM 11 R2. This post is also part of the OIM 11g Academy Series.
With the introduction of the Catalog, request creation process changed from a wizard to a shopping cart experience style. But request pre-populating is still a common requirement for OIM customers.
There are two different approaches to pre-populate a request:
With the introduction of the Catalog, request creation process changed from a wizard to a shopping cart experience style. But request pre-populating is still a common requirement for OIM customers.
There are two different approaches to pre-populate a request:
- Pre-populate plug-ins
- UI customization
Friday, January 4, 2013
OIM 11g R2 Requests Lifecycle Management API’s
Introduction
OIM 11g R2 being such a comprehensive provisioning solution,
it provides API’s for almost every aspect of functionality available in the
product. This makes it a little difficult to decide which examples are needed
the most in the documentation. Fortunately, the documentation does supply
samples that can definitely serve as a foundation for more complex pieces of
code. Some of the API’s I found developers using more often than others are the
ones related to the operations associated with users’ requests for resources.
Amongst those the following API’s are mostly required:
- Request Creation/Submission
- Request History Data Access
- Child Table Data Manipulation
- Approval Information Data Access
This blog post will include a few samples on how to
accomplish each one of the above mentioned operations within the context of a
use case described shortly. The intent is to provide some useful API’s code samples
that customers and partners can use to write their own custom code that
requires such functionality.
Thursday, January 3, 2013
Authenticating OIM APIs without end user's password
A common requirement in an OIM implementation is to not expose OIM user interface to all types of end users. To address this requirement, usually a custom application using OIM APIs is developed and deployed. Such application will expose specific OIM functionalities to end users. In most of the cases, customers want the custom application/OIM APIs to act as the end user, and not as a service account; this approach leverages OIM security model, and the actions will be correctly audited in OIM. Usually this custom application will be protected by a SSO
solution, and asking the end user to provide his/her password is not an
option. So the big question is: how to authenticate the OIM APIs against OIM server and make them act as the end user?
This is another post in the OIM Academy series. To view the entire OIM 11g Academy series click here
In OIM 9.x, the APIs provide two different ways of authentication: through OIM user's credentials (username and password) and through the so called digital signature authentication. The digital signature authentication process allows authentication without a password, and because of that it is a largely used approach in custom OIM APIs based applications.
With the introduction of OIM 11g, the digital signature APIs are being deprecated. They will still work when correctly configured, but they may be discontinued in future OIM releases.
In R2 there is an easier way of using OIM APIs without the need of end's user password. This post shows how this can be done.
This is another post in the OIM Academy series. To view the entire OIM 11g Academy series click here
In OIM 9.x, the APIs provide two different ways of authentication: through OIM user's credentials (username and password) and through the so called digital signature authentication. The digital signature authentication process allows authentication without a password, and because of that it is a largely used approach in custom OIM APIs based applications.
With the introduction of OIM 11g, the digital signature APIs are being deprecated. They will still work when correctly configured, but they may be discontinued in future OIM releases.
In R2 there is an easier way of using OIM APIs without the need of end's user password. This post shows how this can be done.
Wednesday, December 26, 2012
OIM 11g R2 UI Customization Tips and Tricks
Introduction
OIM 11g R2 has finally provided OIM Developers with the
means to implement very sophisticated and functional rich customizations to the
Out of the Box User Interface of OIM; and the best part is, all these
customizations are patching and upgrade transparent, which means that when the
OIM installation is upgraded or patched, the customizations don’t have to be
re-applied. Everything is stored in the metadata repository (MDS) and it is
applied on top of the standard user interface. This article presents a few
techniques to implement customizations that go a little beyond the capabilities
of Web Composer; but still are within the scope of OIM’s MDS. Each technique
will be presented in the context of a use case addressed by the customization implemented using the given technique.
On a recent post by Daniel Gralewski, there was a very nice
customization for the Catalog. The purpose of such customization was to filter
the resources already provisioned to a user from the results of a catalog
search. In a follow up question, one of our readers asked if the search screen
could be customized to add a drop down box that can be used to trigger a
predefined search, like a catalog search based on role category.
So I thought that would be a nice use case to start, here is what I envisioned based on certain requirements from an actual customer I am helping at the present time.
So I thought that would be a nice use case to start, here is what I envisioned based on certain requirements from an actual customer I am helping at the present time.
Monday, October 8, 2012
OAM and OIM 11g Academies
As many of you know, last year we created indexes of posts on OAM and OIM 11g R2 that we call OAM 11g Academy and OIM 11g Academy.
These indexes contain the articles we’ve written that we believe provide long lasting guidance on OAM and OIM. Posts covered in these series include articles on key aspects of OAM and OIM 11g, best practice architectural guidance, integrations, and customizations.
It is our hope that these series will prove valuable to new and experience architects, implementers, and administrators of OAM and OIM.
These indexes contain the articles we’ve written that we believe provide long lasting guidance on OAM and OIM. Posts covered in these series include articles on key aspects of OAM and OIM 11g, best practice architectural guidance, integrations, and customizations.
It is our hope that these series will prove valuable to new and experience architects, implementers, and administrators of OAM and OIM.
Tuesday, September 11, 2012
OIM 11g R2 Catalog
The Catalog is one of most commented new features in OIM 11g. It introduces a new way to search items and to create access requests and it also introduces the ‘shopping cart’ experience.
The request process was drastically simplified with the Catalog. Whereas in OIM 11g R1 users have to go through a multiple step wizard to create a request, in OIM 11g R2 the work is done in two pages: the catalog search and the shopping cart summary.
The request process was drastically simplified with the Catalog. Whereas in OIM 11g R1 users have to go through a multiple step wizard to create a request, in OIM 11g R2 the work is done in two pages: the catalog search and the shopping cart summary.
Tuesday, July 17, 2012
OIM & Connector Server
New versions of OIM connectors have been released in the
past few months(version
number is 11.1.1.x). These new releases bring
an important change to OIM connectors: they are based on the Identity Connector
Framework (IFC). The 11.1.1.5 documentation for the ICF is available at:
One of the things that ICF brings is the capability of
deploying connectors to an ‘Identity Connector Server’(but keep in mind you still need to deploy the connector to OIM as well). When using a connector
server, OIM will delegate to the connector server the execution of the provisioning
tasks. Except for the .NET based connectors (like AD and Exchange), the
connector server is an optional piece in an OIM topology and its use depends on the project requirements.
Friday, July 13, 2012
Oracle Identity Management 11g R2 Launch Webcast
The 11g R2 release of the Oracle Identity Management stack is upon us. The 11g R2 release greatly expands the capabilities of the stack, especially in the area of cloud and mobile environments. On Thursday, July 19 at 10am PST / 1pm EST there will be an interactive Oracle Identity Management 11g R2 launch webcast hosted by Oracle product development executives Hasan Rizvi and Amit Jasuja.
Register now for the interactive launch Webcast, and don’t miss this chance to have your questions answered by Oracle product experts.
Register now for the interactive launch Webcast, and don’t miss this chance to have your questions answered by Oracle product experts.
Monday, April 23, 2012
Custom transformation provider for OIM GTC connector
GTC based connector is one of the most used approaches for reconciling data into OIM, specially through the use of flat files. A common issue is that some customers do not allow direct communication between OIM and the HR system (for different reasons like outsourced HR system, security constraints and others), hence a flat file is made available to OIM so that it reconcile users.
Very often, there is a need to manipulate the data to be reconciled in OIM through the GTC connector. When that is true, most of customers end up creating event handlers to manipulate reconciled data. The problem with this approach is that in OIM 11g, only 'post process' event handlers can be used to manipulate reconciliation data (and the data can only be manipulated after reconciled into OIM), and this can make some manipulations really tricky and/or cumbersome.
Very often, there is a need to manipulate the data to be reconciled in OIM through the GTC connector. When that is true, most of customers end up creating event handlers to manipulate reconciled data. The problem with this approach is that in OIM 11g, only 'post process' event handlers can be used to manipulate reconciliation data (and the data can only be manipulated after reconciled into OIM), and this can make some manipulations really tricky and/or cumbersome.
Tuesday, March 27, 2012
Live webcast (April 11th) with ING on their OIA-OIM implementation
Scale Up Without Getting Bogged Down
If your organization is like many, you’ve conducted access certification for a handful of applications. But what about the other thousand applications? Organizations are spending up to 40% of their IT budgets on compliance, yet many chief information security officers don’t feel any safer than they were before. With the large volume of systems, applications, users, and entitlements to review, the process is error-prone and difficult.
In this session, Mark Robison of ING shares his learning experiences on how to address these challenges. He will discuss how to:
- Simplify the user experience and achieve better service levels
- Reduce the help-desk workload with closed-loop remediation
- Scale the process of certifying applications
- Strike a balance between security risk and audit compliance
https://event.on24.com/eventRegistration/EventLobbyServlet?target=registration.jsp&eventid=389882&sessionid=1&key=DA263A8A48EC01E1F41904939FFC7C56&partnerref=evite_sec_idmmulti42012&sourcepage=register
Tuesday, March 20, 2012
Encapsulating OIM API’s in a Web Service for OIM Custom SOA Composites
Introduction
This document describes how to encapsulate OIM API calls in a Web Service for use in a custom SOA composite to be included as an approval process in a request template.
We always recommend customers to follow this approach when trying to invoke OIM’s APIs inside SOA composites used as approval processes for the following reasons:
- A web service implementation allows the instantiation of all related APIs once at service startup as opposed to getting a remote reference to each required API interface. This improves performance and reduces the memory footprint of the composite if these API’s are instantiated in embedded Java Tasks.
- This paradigm allows the implementation of HA for the Web Service encapsulating the API calls and provides the ability to deploy the web service in a separate server from the SOA and OIM servers is so desired. This increases the robustness and reliability of the solution.
- According to BPEL’s documentation Embedded Java Tasks should only be used for quick utility logic, no business logic should be included in these tasks. For details refer to http://docs.oracle.com/cd/E15586_01/integration.1111/e10224/bp_java.htm#BABHJHBG section 13.2.3 How to Embed Java Code Snippets into a BPEL Process with the bpelx:exec Tag. The reason for that is because all memory required for objects being instantiated within the embedded Java code is adding to the memory space of the composite instance itself which will be kept for the life of the composite instance. This means that if a composite has an asynchronous BPEL process (which is definitely the case for OIM’s Approval Process composites) and that can make the BPEL process to remain there for days or weeks, memory problem may start to arise.
Procedure
The assumption here is that JDeveloper is going to be used to edit the SOA composite and there are no other tools suitable for this purpose. JDeveloper is also a good tool to create the Web Service wrapping the OIM API calls. All that is needed is to create a POJO (Plain Old Java Object) and convert it to a Web Service, and then deploy it to an application server (Weblogic in this case); all of which can be accomplished with JDeveloper.
Please refer to JDeveloper 11g documentation for information on how to create a Web Service out of a POJO since this is out of scope for this document. Once the web service is created and deployed one can obtain the WSDL from the Web Logic Admin console. Just access the deployments and drill down to the Test Client of the web service. The WSDL will be available from the Test client window or from the table showing the testing points in the Weblogic Admin Console. All that is needed is to copy the URL for the WSDL and paste it in the proper text box when configuring the Web Service reference in the composite.
Once the Web Service reference is configured in the Composite, it can be linked to the BPEL process inside the composite. All we need to do is to connect the icon representing the BPEL process with the Web Service reference by stretching an arrow connecting the two of them. Consult the SOA Composite Editor documentation from JDeveloper’s 11g users guide. To invoke methods on the newly wired in Web Service an Invoke Task must be included for each method to be called. The Invoke Task allows you to define the following elements:
- An input variable that will include the input values for the specific method call taken from the WSDL of the Web Service.
- An output variable that will receive the returning data from the invocation of the Web Service method formatted as specified by the WSDL of the Web Service.
Before an invocation there typically is an Assign Task that will populate the input parameters of a Web Service call by copying values from other variables or assigning literal values to the input parameters in the Input Variable. So inserting the Invoke Task prior to inserting the Assign Task allows you to create the Input and Output Variables that will be populated by the Assign Task for the case of the Input Variable and with the output data from the Web Service method call in the case of the Output Variable. Now the values in the Output Variable can be used anywhere else in the composite and can be transferred using other Assign Tasks within the BPEL Process flow.
Summary
SOA Suite allows the execution of embedded Java logic within the composites. OIM Java APIs are not a good candidate to be included in Embedded Java Tasks, especially if the composites are meant to serve as approval processes that can potentially keep instances of the composite for a long time. The recommended approach is encapsulating the OIM APIs in Web Services with a SOAP interface. Then invoke operations on the OIM API Wrapping Web Service and just manipulate the results. This allows for other benefits from the architecture design perspective and from the performance and memory footprint stand point as well to prevent Out of Memory issues.
Friday, March 16, 2012
OIM 11g LDAPSync Deployment Guidelines
OIM 11g can be configured to maintain its user and role population synchronized with an LDAP directory using the LDAPSync feature. This functionality is based on asynchronous processing through orchestration events from OIM to LDAP and on scheduled tasks for synchronization from LDAP to OIM. This approach could mean that at some point in time, some of the entries on both repositories may be out-of-sync. Specially when executing long running Trusted Reconciliation scheduled jobs. The entry differences can be caused by processing errors or time lapse between user creation in OIM and user creation in LDAP. This post details some guidelines to minimize and troubleshoot possible errors for OIM LdapSync.
Consider upgrading to OIM 11.1.1.5.2 (OIM 11g Bundle Patch 02). BP02 provides a number of fixes that improve stability specially during bulk processing (large trusted reconciliations).
Tuning and Tips
Tune the environment to allow for better ldapsync performance when executing large trusted reconciliation jobs in the order of +30K. These are some tuning tips, some of them straight from the documentation, others from existing deployments.
OIM Tuning
1. JVM: PORT_MEM_ARGS="-Xms768m -Xmx2048m" in setSOADomainEnv.sh
2. MDBs: In WLS Admin Console -> Environment->Worker Managers->MaxThreadsConstraints-1 set count to 100
3. Disable reloading of Adapters: Using weblogicExportMetadata.sh and weblogicImportMetadata.sh edit the MDS file /db/oim-config.xml.
Replace:
<ADPClassLoaderConfig adapterReloadingEnabled="true" loadingStyle="ParentFirst" reloadInterval="15" reloadingEnabled="true">
With:
<ADPClassLoaderConfig adapterReloadingEnabled="false" loadingStyle="ParentFirst" reloadInterval="15" reloadingEnabled="false">
And
<storeConfig reloadingEnabled="true" reloadingInterval="20"/>
With:
<storeConfig reloadingEnabled="false" reloadingInterval="20"/>
4. Database: Monitor Perfomance with AWR reports and collect complete schema statistics using:
DBMS_STATS.GATHER_SCHEMA_STATS(OWNNAME=> schema_owner,
ESTIMATE_PERCENT=>DBMS_STATS.AUTO_SAMPLE_SIZE,
DEGREE=>8,
OPTIONS=>'GATHER AUTO',
NO_INVALIDATE=>FALSE);
OID Tuning
- Consider deploying multiple OID instances for Failover and Load Balancing. Front end the instances with an LB
- Number of OID LDAP Server Processes = #cpus. EM -> Administration -> Server Properties -> Performance ( for each oid instance)
- Number of DB Connections per Server Process = 10 (orclmaxcc). EM -> Administration ->server properties (for each oid instance)
- Check Skip Referral for Search. EM -> Administration -> Shared Properties (Only if not using referrals in OID).
OVD Tuning (assuming no libOVD is used)
- Consider deploying multiple OVD instances for Failover and Load Balancing. Front end the instances with an LB and use the OID LB virtual host as the LDAP server host.
- The parameter Operations Timeout for the Adapters to 30000 if needed (using ODSM)
- Consider increasing maxpoolsize for the Adapters to 30-40 if needed (using ODSM)
LDAPSync Monitoring
During the time when the LdapSync Orchestration is running check the following tables and columns in the OIM Schema to verify processing:
Obtain the latest reconciliation job key (RJ_KEY) with the query:
select max(RJ_KEY) from recon_events;
Table RECON_BATCHES: using RJ_KEY and RB_NOTE verify that the orchestration events are being created. The Column RB_NOTE shows the orchestration Process ID and the operation. It could also show errors that occur.
Table ORCH_PROCESS: Holds the generated orch processes. ID being the Orchestration Process ID. If Status shows Compensated it means that an event failed. The detail can be seen in the table ORCH_EVENTS.
Table ORCH_EVENTS: Linked to the orchestration process with the column PROCESSID. The RESULT column has the error details in case of failure.
The Out-of-the-Box reconciliation job " Retry Failed Orchestrations " can be used to retry compensated orchestration processes. Specify a date range ("ddMMyyyy") for multiple ones or "Orchestration ID" for single ones. OIM BP02 also includes fixes for this task.
Note: In the case when reconciling new users that come as disabled, an existing bug may create the orchestration disable event before the orchestration create event. So, these disable events would fail in LDAP since the user doesn't exist yet. As a workaround, these events can be retried with the above Recon Job (specify OPERATION=DISABLE and a date range) after all users are created in LDAP.
Thursday, November 17, 2011
OIM 11g OID (LDAP) Groups Request-Based Provisioning with custom approval – Part II
Introduction 
Wls_servername is the name of the managed server as you defined it in the WebLogic Domain.
Application_name is always ‘oim’.
Metadata_from_loc is the path to the directory created in the first step. Specify this path omitting the last directory in the path (‘file’) as shown in the figure. So if you have a directory /opt/fmw11g/Oracle_IDM1/DataSet/file then the path should be specified as /opt/fmw11g/Oracle_IDM1/DataSet.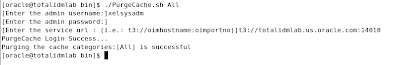 In this case the user has to be xelsysadm instead of weblogic.
This is Part Two of the article describing a potential implementation of Request Based LDAP Group Membership provisioning. Part One can be accessed here.
Continuing with the implementation after disabling the default approval policies at the Request and Operation Levels, the next step is to configure OIM to enable the modification of a provisioned resource via a request. The datasets associated to the Create and Modify operations of the resource in questions (OID User in this case) have to be imported into MDS. The connector’s installer at the present time doesn’t do the import of the metadata files to enable request based operations for the connector; this has to be done after installation by running the corresponding MDS utilities available in OIM.
Importing Connector’s Data Sets into MDS
The files containing the definition of the data collected by the Provisioning operations are called data sets. For OID User, there are two DataSet XML files:
- ModifyResourceOID User.xml
- ProvisionResourceOID User.xml
The one that we will need is the ModifyResourceOID User.xml. Here is the data set below:

From this data set this is what we will need for our implementation:
‘OID User Groups’ will be used as the attribute name to construct the RequestBeneficiaryEntityAttribute as shown in the code snippet below:

If you see any required attributes in the data set, you will have to create a value for the RequestBeneficiaryEntityAttribute for that attribute reference in the data set. The OID Server is one of those attributes. Also for the insertion of Child table records here is the specific code fragment for that:

Notice that we have to use the actual Database Table field name which can be retrieved from the Form Definition. See below:

Uploading DataSets into MDS
In this section I describe the process to upload DataSet XML files into MDS for OIM to use in Request Based Provisioning. As most of you know Data Sets determine the Fields collected during the provisioning process and certain attributes of those fields that make them required, pre-populated or only visible to the approvers. We won’t get into the details of the structure of the data sets involved here but at least we will cover a simple procedure for importing them into MDS. MDS is the acronym for Meta Data Store. Many applications part of the Fusion Middleware family rely on MDS to store configuration or Application Metadata.
This implementation works with OID’s data sets so this is the procedure to import them into MDS:
- Create a directory inside
/ / called DataSet/file (i.e in my case the directory is /opt/fmw11g/Oracle_IDM1/DataSet/file where my Middleware Home is /opt/fmw11g and my OIM installation resides under Oracle_IDM1 directory). - Copy all the datasets from the connector’s binaries home into the directory you just created in the previous step.
- Switch to the bin directory inside the server directory under you OIM home directory (i.e. in my case /opt/fmw11g/Oracle_IDM1/server/bin).
- Modify the file weblogic.properties inside the directory mentioned above. Here is mine:

Wls_servername is the name of the managed server as you defined it in the WebLogic Domain.
Application_name is always ‘oim’.
Metadata_from_loc is the path to the directory created in the first step. Specify this path omitting the last directory in the path (‘file’) as shown in the figure. So if you have a directory /opt/fmw11g/Oracle_IDM1/DataSet/file then the path should be specified as /opt/fmw11g/Oracle_IDM1/DataSet.
- Set the OIM_ORACLE_HOME to your OIM installation Home (i.e. in my case this is what I did export OIM_ORACLE_HOME=/opt/fmw11g/Oracle_IDM1).Run the weblogicImportMetadata.bat|sh script. The script will ask the following:
- User name: weblogic (Do not use xelsysadm)
- Password:
- Server URL: t3://myOIMHost
:14000 # Provide the URL to your oim managed server and oim's port. You should get an output similar to the one described below:

Run the script PurgeCache.bat|sh. Before running the script you need to set WL_HOME and JAVA_HOME environment variables with your location of WebLogic Server installation directory and path to a valid Java JDK/JRE directory (i.e. WL_HOME=/opt/fmw11g/wlserver_10.3 and JAVA_HOME=/opt/fmw11g/jdk160_24 coming with my FMW installation). The output should be similar to the following:

 In this case the user has to be xelsysadm instead of weblogic.
Configuring the Human Task (Custom Approval Process SOA Composite)
Now it is time to look in detail at the SOA Composite that will serve as an approval process for our entitlements (LDAP Groups). Look at the following set of pictures:

From the Composite.xml design view in JDeveloper, right click on the Green Human Task icon and select Edit.

Select the Participant block and the click the Edit button at the top of the screen. This brings the screen shown below:

Notice the Value Column of the participant selection table. It is a User whose Login ID is retrieved from the payload in this case: /task:task/task:ownerUser. This is populated in the early stages of the composite right after the corresponding approver is retrieved from the Entitlements_Staging Database table for the requested Entitlement identified by the field EntitlementID. This information is retrieved by the Database Adapter Web Service configured to execute a query against the Entitlements_Staging table part of the schema defined in our solution. For information on how to configure the Database Adapter task in a BPEL process, see the documentation for Fusion Middleware – SOA Suite.
Summary
In summary this post describes a potential approach to implement Request Based OID User Group Membership provisioning using a custom approval process.
The concepts shown in this post include:
- A description of OIM API’s to construct and submit requests to modify provisioned resource.
- A demonstration of the process of configuring Custom Approval Processes via Request Templates.
- A description of the OIM configuration required to disable the default Request and Operation level approvals.
- The steps necessary to customize the SOA composite to extract required Entitlement and Associated Approver information and how to set up the Participants of the Human Task used to Approve/Reject requests.
- The steps to import metadata required to enable request based provisioning for OID Resource Objects (Users and Groups).
For further details about configuration of OIM for Provisioning Processes, Process Forms, Access Policies and any details mentioned but not covered in detail in this post please access OIM Fusion Middleware Documentation from the Fusion Middleware 11g documentation.
Subscribe to:
Posts (Atom)

 Posts